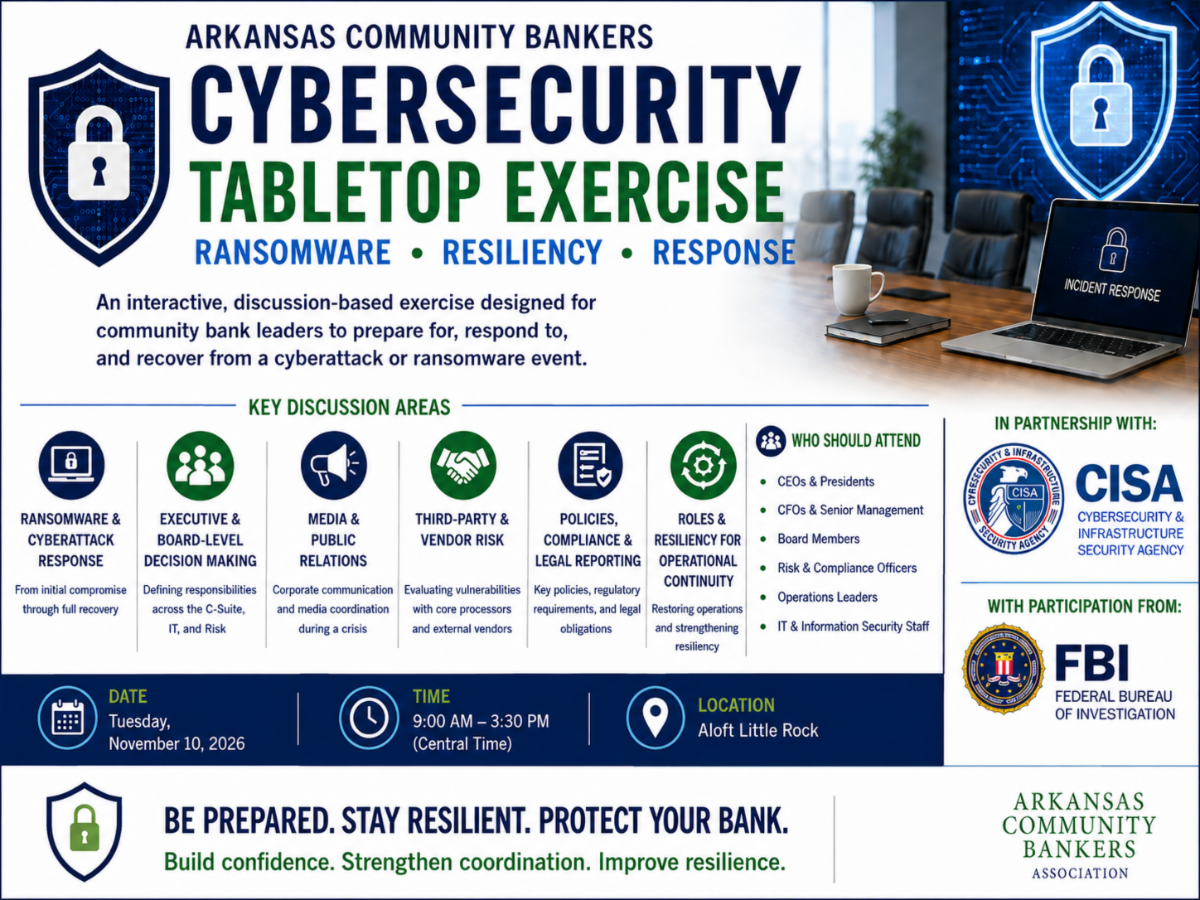
Arkansas Community Bankers Tabletop Exercise Agenda Cyber/Ransomware Incident Response & Resiliency Time: 9:00 AM – 3:00 PM Format: Discussion-based tabletop exercise Focus: Ransomware response, communications, vendor risk, compliance, internal roles, and recovery 9:00 AM – 9:15 AM Welcome and Opening Remarks
- Welcome from Arkansas Community Bankers Association
- Overview of the purpose of the tabletop exercise
- Introductions of facilitators, participants, and observers
- Review of exercise expectations and discussion format
9:15 AM – 9:30 AM Exercise Objectives and Scenario Briefing
- Review tabletop objectives
- Explain the ransomware/cyberattack scenario
- Discuss expected participant roles
- Confirm focus areas:
- Incident response
- Communication
- Vendor coordination
- Compliance and reporting
- Recovery and resiliency
9:30 AM – 10:30 AM Module 1: Initial Compromise and Incident Discovery
- Scenario begins with suspected cyber compromise
- Identification of early warning signs
- Internal escalation procedures
- Role of IT, operations, risk management, and executive leadership
- Initial decision-making by bank management
10:30 AM – 10:45 AM Break 10:45 AM – 11:30 AM Module 2: Ransomware Escalation and Operational Disruption
- Ransomware confirmed
- Impact on bank systems, customer access, and daily operations
- Business continuity considerations
- C-Suite and board-level involvement
- Coordination between IT, management, compliance, and risk
11:30 AM – 12:00 PM Module 3: Third-Party and Vendor Risk
- Core processor and IT vendor dependencies
- Managed service provider concerns
- Vendor communication during an active incident
- Contracting, response obligations, and service restoration
- Discussion with vendor risk observer or subject-matter expert
12:00 PM – 12:30 PM Lunch / Working Discussion
- Informal discussion among participants
- Optional remarks from external experts or observers
12:30 PM – 1:15 PM Module 4: Media, Public Relations, and Customer Communication
- Who speaks on behalf of the bank
- Public messaging during a crisis
- Media inquiries and customer confidence
- Coordination between management, legal counsel, and communications staff
- PR speaker may participate as an observer and provide feedback during the hotwash
1:15 PM – 2:00 PM Module 5: Bank Policies, Compliance, and Legal Reporting
- Incident response policy expectations
- Business continuity and disaster recovery plans
- Regulatory notification requirements
- Documentation during the incident
- Legal, compliance, and board reporting considerations
- Compliance or legal expert may observe and provide feedback during hotwash
2:00 PM – 2:15 PM Break 2:15 PM – 2:45 PM Module 6: Recovery, Resiliency, and Law Enforcement Coordination
- Recovery from ransomware event
- Restoration of operations
- Lessons learned during the recovery phase
- When and how to involve the FBI
- Law enforcement coordination and ransom-related considerations
- Long-term resiliency improvements
2:45 PM – 3:00 PM Hotwash and Closing Discussion
- Facilitator-led review of key takeaways
- Feedback from CISA
- Observations
- Identification of policy, communication, vendor, and response gaps
- Recommended next steps for participating banks
- Closing remarks
|